OpenAI Trains Staff on Espionage Risks, Warns Against Company Logo Wear
MissedBlock Desk · · 4 min read
Updated
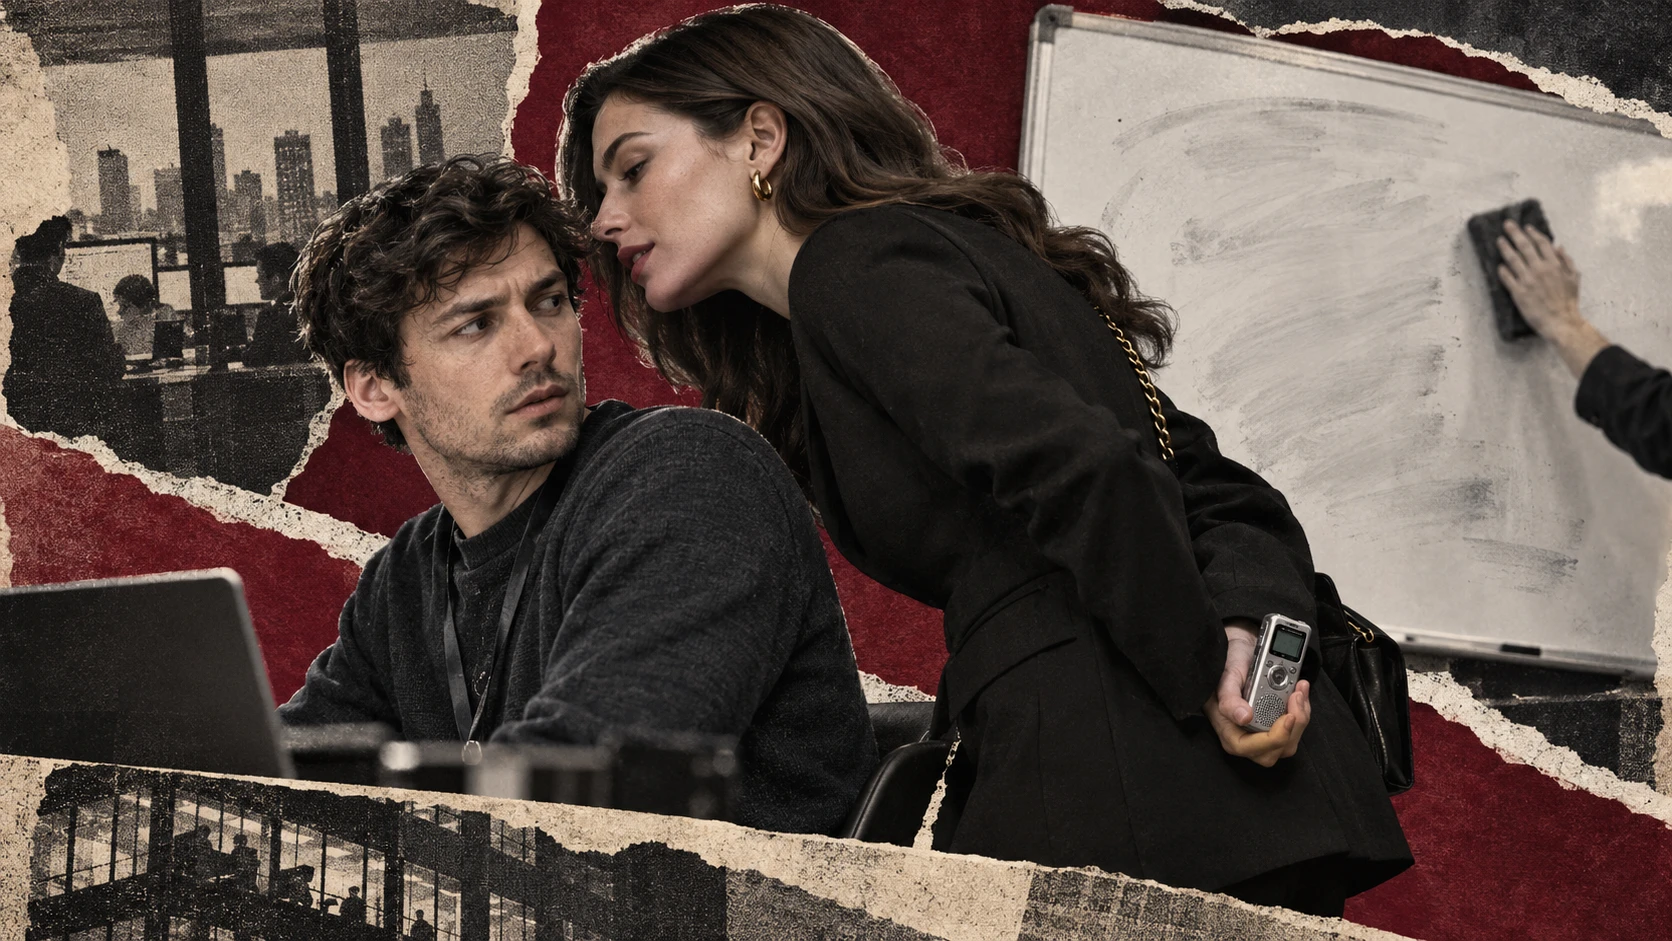
OpenAI Warns Staff Against ‘Honeypot’ Spies and Workplace Security Lapses
OpenAI has been reminding its employees about potential espionage tactics, including the risk of being lured by individuals posing as romantic interests, and the importance of erasing whiteboards after meetings. Similar warnings have also been heard by employees at Anthropic and Google, according to The Wall Street Journal.
These internal training directives have come to light following the arrest of OpenAI engineer Abdulrahman Alfozan on October 9th for allegedly planting a recording device in a company conference room. The Wall Street Journal subsequently reported on the training materials, noting that employees at rival AI firms Anthropic and Google have received comparable advisories.
A particularly striking piece of advice from OpenAI’s training involves vigilance against “honeypot” spies, who use sexual or romantic relationships to gain access to targets. The company has reportedly cautioned employees in some internal sessions that individuals attempting to seduce them could be operating in this capacity. Erin Woo, a reporter for The Wall Street Journal, summarized this point on X (formerly Twitter): “If someone is trying to seduce you, first consider — could they be a spy???”
The training also recounted an incident where an OpenAI employee was approached by a stranger at a San Francisco playground while with their child. The conversation, initially casual, gradually steered towards the employee’s work. The Wall Street Journal described this as more than mere curiosity, suggesting the stranger was an operative.
OpenAI has also shared an anecdote about a foreign intelligence agency’s approach to a U.S. diplomat in Russia. The tactic involved sending a blonde woman with champagne to his hotel room, followed by a redhead and then a young man, after his initial rejection.
Security personnel have also emphasized two key concerns: the potential for individuals to be paid for commercial secrets, and the risk of conversations being overheard in public spaces like coffee shops. More routine security protocols include advice against wearing company-branded clothing outside the office, using privacy screens on phones and laptops when using public transport, and diligently erasing whiteboards after meetings, even within the office, to prevent information from being compromised by cleaning staff who might be coerced.
The recent high-profile recording device incident is understood to be a significant catalyst for these renewed security measures.
The arrested engineer, 35-year-old Abdulrahman Alfozan, a Saudi national, had been employed at OpenAI as an engineer since July 2025 and has since been terminated. OpenAI discovered a recording device wrapped in tissue paper behind a television in a high-level conference room during a scan on September 30th. Alfozan faces charges of eavesdropping, which carries a maximum penalty of five years in prison and a $250,000 fine. He has not been charged with stealing trade secrets or working for a foreign government.
While OpenAI has stated there is no indication that Alfozan accessed or removed model weights, source code, or customer data, new developments have emerged regarding his travel plans. In a filing on October 8th, prosecutors requested that the complaint remain sealed, citing that Alfozan, his wife, and another family member had booked one-way tickets from San Francisco to Saudi Arabia via Istanbul for October 12th. Prosecutors believe this indicates his ability and motivation to flee the country prematurely. His next court appearance is scheduled for October 19th.
OpenAI’s tightening of security measures is not entirely new. The Financial Times reported in July of last year that OpenAI had enhanced its security protocols in January 2025, following the launch of DeepSeek’s model. These measures included storing confidential technology on air-gapped computers, requiring fingerprint scans for access to sensitive areas, and implementing a default company network policy that prohibits external connections without individual approval.
The question of whether external actors are actively targeting AI companies remains a concern. Randy Watt, a representative from SRW, a firm that advises corporate executives, told The Wall Street Journal, “Catching one person means there are five or six others out there.” He added that the targets may not only be technical or strategic information but also personal data that could be used for exploitation or blackmail.